

Splunk SPLK-3001 Practice Test Pdf Exam Material
SPLK-3001 Answers SPLK-3001 Free Demo Are Based On The Real Exam
NEW QUESTION # 51
Which settings indicated that the correlation search will be executed as new events are indexed?
- A. Always-On
- B. Real-Time
- C. Continuous
- D. Scheduled
Answer: D
Explanation:
Reference:
https://docs.splunk.com/Documentation/ES/6.1.0/Admin/Configurecorrelationsearches
NEW QUESTION # 52
The Brute Force Access Behavior Detected correlation search is enabled, and is generating many false positives. Assuming the input data has already been validated. How can the correlation search be made less sensitive?
- A. Edit the search and modify the notable event status field to make the notable events less urgent.
- B. Edit the search, look for where or xswhere statements, and alter the threshold value being compared to make it a more common match.
- C. Modify the urgency table for this correlation search and add a new severity level to make notable events from this search less urgent.
- D. Edit the search, look for where or xswhere statements, and after the threshold value being compared to make it less common match.
Answer: D
Explanation:
Explanation
If the number of failed logins is greater than or equal to the threshold value, the search triggers a notable event.
To make the search less sensitive, the threshold value can be increased, so that only more frequent failed logins will trigger a notable event. For example, the default threshold value is 4, which means that 4 or more failed logins within a 1-minute window will trigger a notable event. If the threshold value is changed to 10, then only 10 or more failed logins within a 1-minute window will trigger a notable event. References = Splunk Enterprise Security Admin Manual Detecting brute force access behavior
NEW QUESTION # 53
How is notable event urgency calculated?
- A. Alert severity found by the correlation search.
- B. Asset priority and threat weight.
- C. Asset or identity risk and severity found by the correlation search.
- D. Severity set by the correlation search and priority assigned to the associated asset or identity.
Answer: D
NEW QUESTION # 54
How is it possible to navigate to the list of currently-enabled ES correlation searches?
- A. Configure -> Correlation Searches -> Select Status "Enabled"
- B. Settings -> Searches, Reports, and Alerts -> Select App of "SplunkEnterpriseSecuritySuite" and filter by "- Rule"
- C. Configure -> Content Management -> Select Type "Correlation" and Status "Enabled"
- D. Settings -> Searches, Reports, and Alerts -> Filter by Name of "Correlation"
Answer: C
NEW QUESTION # 55
Which of the following is a risk of using the Auto Deployment feature of Distributed Configuration Management to distribute indexes.conf?
- A. Indexes might be processing.
- B. Indexes might crash.
- C. Indexes have different settings.
- D. Indexes might not be reachable.
Answer: B
Explanation:
Reference:
https://docs.splunk.com/Documentation/Splunk/8.0.2/Admin/Indexesconf
NEW QUESTION # 56
Who can delete an investigation?
- A. The investigation owner and ess-admin.
- B. The investigation owner and collaborators.
- C. ess_admin users only.
- D. The investigation owner only.
Answer: C
Explanation:
Explanation/Reference: https://docs.splunk.com/Documentation/ES/6.1.0/Admin/Manageinvestigations
NEW QUESTION # 57
Which of the following lookup types in Enterprise Security contains information about known hostile IP addresses?
- A. Threat intel.
- B. Assets.
- C. Domains.
- D. Security domains.
Answer: A
Explanation:
Explanation
Threat intel is the lookup type in Enterprise Security that contains information about known hostile IP addresses, as well as other indicators of compromise (IOCs) such as domains, URLs, hashes, and email addresses. Threat intel is collected from various sources, such as Splunk Enterprise Security, Splunk Add-on for Enterprise Security, Splunk Enterprise Security Content Update, and third-party threat intelligence providers. Threat intel is used to enrich events and generate notable events when a match is found between an IOC and an event field. You can view and manage the threat intel sources and lookups in Enterprise Security using the Threat Intelligence framework. References = Threat Intelligence framework in Splunk ES Threat Intelligence overview
NEW QUESTION # 58
When creating custom correlation searches, what format is used to embed field values in the title, description, and drill-down fields of a notable event?
- A. _fieldname_
- B. $fieldname$
- C. %fieldname%
- D. "fieldname"
Answer: B
NEW QUESTION # 59
How does ES know local customer domain names so it can detect internal vs. external emails?
- A. ES uses the User Activity index and applies machine learning to determine internal and external domains.
- B. ES extracts local email and web domains automatically from SMTP and HTTP logs.
- C. Web and email domain names are set in General -> General Configuration.
- D. The Corporate Web and Email Domain Lookups are edited during initial configuration.
Answer: D
Explanation:
Explanation
Splunk Enterprise Security knows the local customer domain names so it can detect internal vs. external emails by using the Corporate Web and Email Domain Lookups. These are lookup files that contain the list of domains that are considered internal or corporate for the organization. The Corporate Web and Email Domain Lookups are edited during the initial configuration of Splunk Enterprise Security, and they are used to enrich events with the tag=internal_web or tag=internal_email fields. These fields indicate whether the web or email activity is internal or external, and they are used by dashboards and correlation searches in Splunk Enterprise Security to monitor and analyze the web and email traffic. References = Corporate Web and Email Domain Lookups Configure web and email domains in Splunk Enterprise Security Detecting Typosquatting, Phishing, and Corporate Espionage ... - Splunk
NEW QUESTION # 60
What kind of value is in the red box in this picture?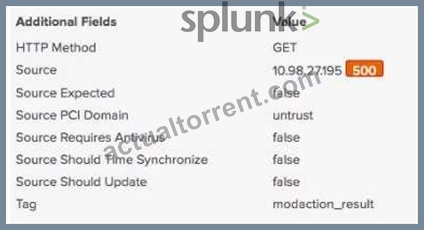
- A. An event priority.
- B. A source ranking.
- C. A risk score.
- D. An IP address rating.
Answer: A
Explanation:
Explanation/Reference: https://docs.splunk.com/Documentation/Splunk/8.0.2/Data/FormateventsforHTTPEventCollector
NEW QUESTION # 61
What does the Security Posture dashboard display?
- A. Active investigations and their status.
- B. A display of the status of security tools.
- C. Current threats being tracked by the SOC.
- D. A high-level overview of notable events.
Answer: D
Explanation:
The Security Posture dashboard is designed to provide high-level insight into the notable events across all domains of your deployment, suitable for display in a Security Operations Center (SOC). This dashboard shows all events from the past 24 hours, along with the trends over the past 24 hours, and provides real-time event information and updates.
Reference: https://docs.splunk.com/Documentation/ES/6.1.0/User/SecurityPosturedashboard
NEW QUESTION # 62
Enterprise Security's dashboards primarily pull data from what type of knowledge object?
- A. Data models
- B. KV Store
- C. Dynamic lookups
- D. Tstats
Answer: A
Explanation:
Explanation
Data models are the primary source of data for Enterprise Security dashboards. Data models provide a structured and consistent way of defining and retrieving data from indexes. Data models accelerate searches by using prebuilt summaries of the data. Data models also enable the use of the tstats command, which can perform statistical analysis on the data model summaries. Data models are mapped to the Common Information Model (CIM), which provides a common language for describing data across domains and technologies. References = About data models Use the Common Information Model in Splunk Web
NEW QUESTION # 63
When creating custom correlation searches, what format is used to embed field values in the title, description, and drill-down fields of a notable event?
- A. _fieldname_
- B. $fieldname$
- C. %fieldname%
- D. "fieldname"
Answer: B
Explanation:
Explanation
When creating custom correlation searches, you can use the fieldname format to embed field values in the title, description, and drill-down fields of a notable event. This allows you to customize the notable event with dynamic information from the search results. For example, you can use src to include the source IP address of the event, or user to include the user name of the event1. References = 1: Create a correlation search - Splunk Documentation - Define the notable event.
NEW QUESTION # 64
What kind of value is in the red box in this picture?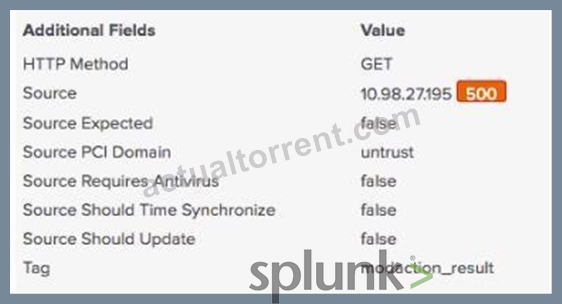
- A. An event priority.
- B. An IP address rating.
- C. A source ranking.
- D. A risk score.
Answer: B
Explanation:
Explanation
The value in the red box is an IP address rating. This is a numerical value that represents the risk associated with an IP address. The higher the value, the higher the risk. This value is calculated based on the number of security events associated with the IP address, the severity of those events, and the time since the last event.
References:
Administering Splunk Enterprise Security
Splunk Enterprise security Admin
IP Intelligence
NEW QUESTION # 65
Where are attachments to investigations stored?
- A. KV Store
- B. notable index
- C. <splunk_home>/etc/apps/SA-Investigations/default/ui/views/attachments
- D. attachments.csv lookup
Answer: A
Explanation:
Reference:
https://docs.splunk.com/Documentation/ES/6.1.0/Admin/Manageinvestigations
NEW QUESTION # 66
What does the Security Posture dashboard display?
- A. Active investigations and their status.
- B. Current threats being tracked by the SO
- C. A display of the status of security tools.
- D. A high-level overview of notable events.
Answer: D
Explanation:
The Security Posture dashboard is designed to provide high-level insight into the notable events across all domains of your deployment, suitable for display in a Security Operations Center (SOC). This dashboard
NEW QUESTION # 67
An administrator wants to ensure that none of the ES indexed data could be compromised through tampering. What feature would satisfy this requirement?
- A. Indexer acknowledgement.
- B. Data integrity control.
- C. Index consistency.
- D. Index access permissions.
Answer: B
Explanation:
Reference:
the.html
NEW QUESTION # 68
The Add-On Builder creates Splunk Apps that start with what?
- A. SA-
- B. App-
- C. TA-
- D. DA-
Answer: C
Explanation:
Explanation/Reference: https://dev.splunk.com/enterprise/docs/developapps/enterprisesecurity/abouttheessolution/
NEW QUESTION # 69
......
SPLK-3001 [Jan-2026] Newly Released] Exam Questions For You To Pass: https://www.actualtorrent.com/SPLK-3001-questions-answers.html
Splunk SPLK-3001 Exam: Basic Questions With Answers: https://drive.google.com/open?id=1-xi-KWcj8kM_uZO79z7X57olijJ6PKNq